Make compliance real
Cyber Essentials, Cyber Essentials Plus and ISO 27001, done the way an assessor will actually test them: evidence from the devices, fixes applied by the people who manage them, and a posture you can see every day rather than once a year.
See how Clearview gets you ready for Cyber Essentials, or all the way to ISO 27001
Your compliance posture as a live status, evidence collected from the devices we manage, the Cyber Essentials Plus checks run on every machine before the assessor does, and CISO Assistant for the management system behind ISO 27001.
What Cyber Essentials now demands
The scheme tightened in April 2026. If your last certificate was issued under the old question set, these are the changes most likely to catch you at renewal.
Danzell is the live question set
New Cyber Essentials assessment accounts have used the v3.3 Danzell question set since 27 April 2026. Remaining Willow (v3.2) accounts must be finalised by 26 October 2026, and any Cyber Essentials Plus linked to a Willow self-assessment by 26 January 2027.
No MFA on a cloud service is an automatic fail
Multi-factor authentication is now mandatory on every cloud service where it is available: email, Microsoft 365 and Google Workspace, admin portals, the lot. Cost or licence tier is no longer an excuse.
Critical and high-risk updates, patched in 14 days
Anything rated CVSS 7.0 or above must be fixed within 14 days of a fix being released. The assessor checks this with an internal vulnerability scan of sampled devices, and missed patches are an auto-fail.
A formal definition of what counts as a cloud service
Danzell defines cloud services and how they are scoped, so there is far less room to leave a SaaS tool out of the assessment. Backups are now called out explicitly, and passwordless authentication is encouraged.
What you must have, and how it is tested
Every Cyber Essentials requirement sits under one of five technical controls. Plus adds an assessor who checks them on your actual devices.
Firewalls
A firewall on every device and at the boundary, with inbound rules reviewed and only required ports open.
The assessor checks host firewalls are on and that nothing unexpected is listening.
Secure configuration
Default accounts and unnecessary software removed, auto-run disabled, device lock within ten minutes of inactivity.
Configuration is reviewed on a sample of devices against what you declared.
User access control
Separate administrator accounts, least privilege, joiners and leavers handled properly, MFA on all cloud services.
MFA is verified on email and core cloud apps; admin separation is checked on devices.
Malware protection
Supported anti-malware or EDR on every device, updating and set to block.
Test files are executed on sampled devices to confirm real-time detection and quarantine.
Security update management
Supported operating systems and software, automatic updates, critical and high fixes within 14 days.
An internal vulnerability scan looks for anything CVSS 7.0+ older than 14 days; an external scan covers internet-facing systems.
The screens you and the assessor will see
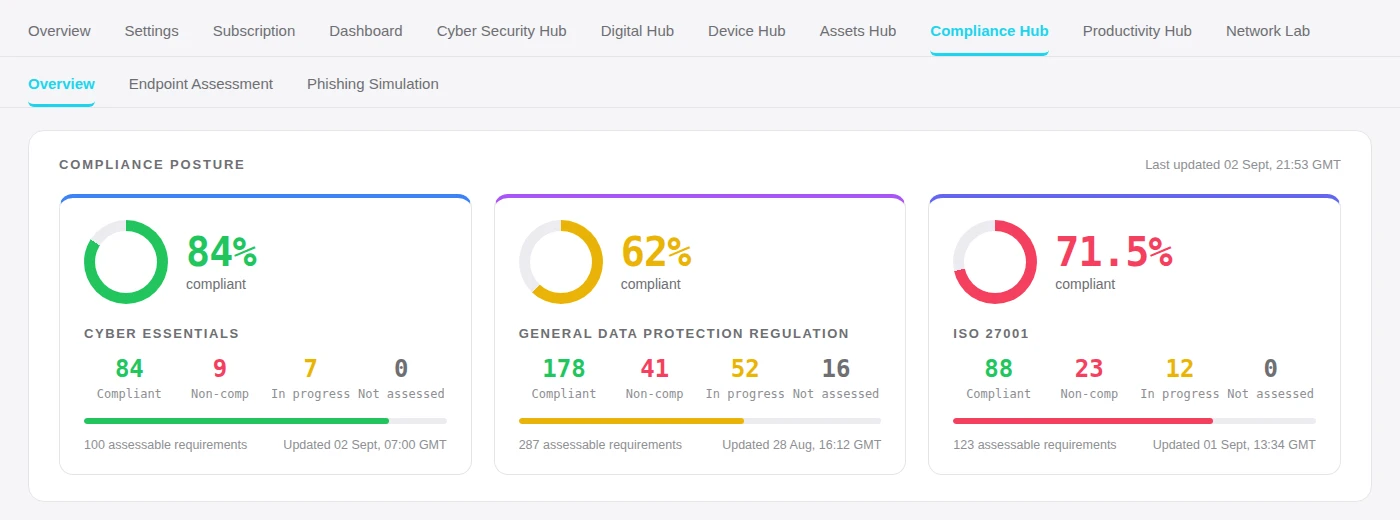
Compliance posture
Cyber Essentials, GDPR and ISO 27001 as live status
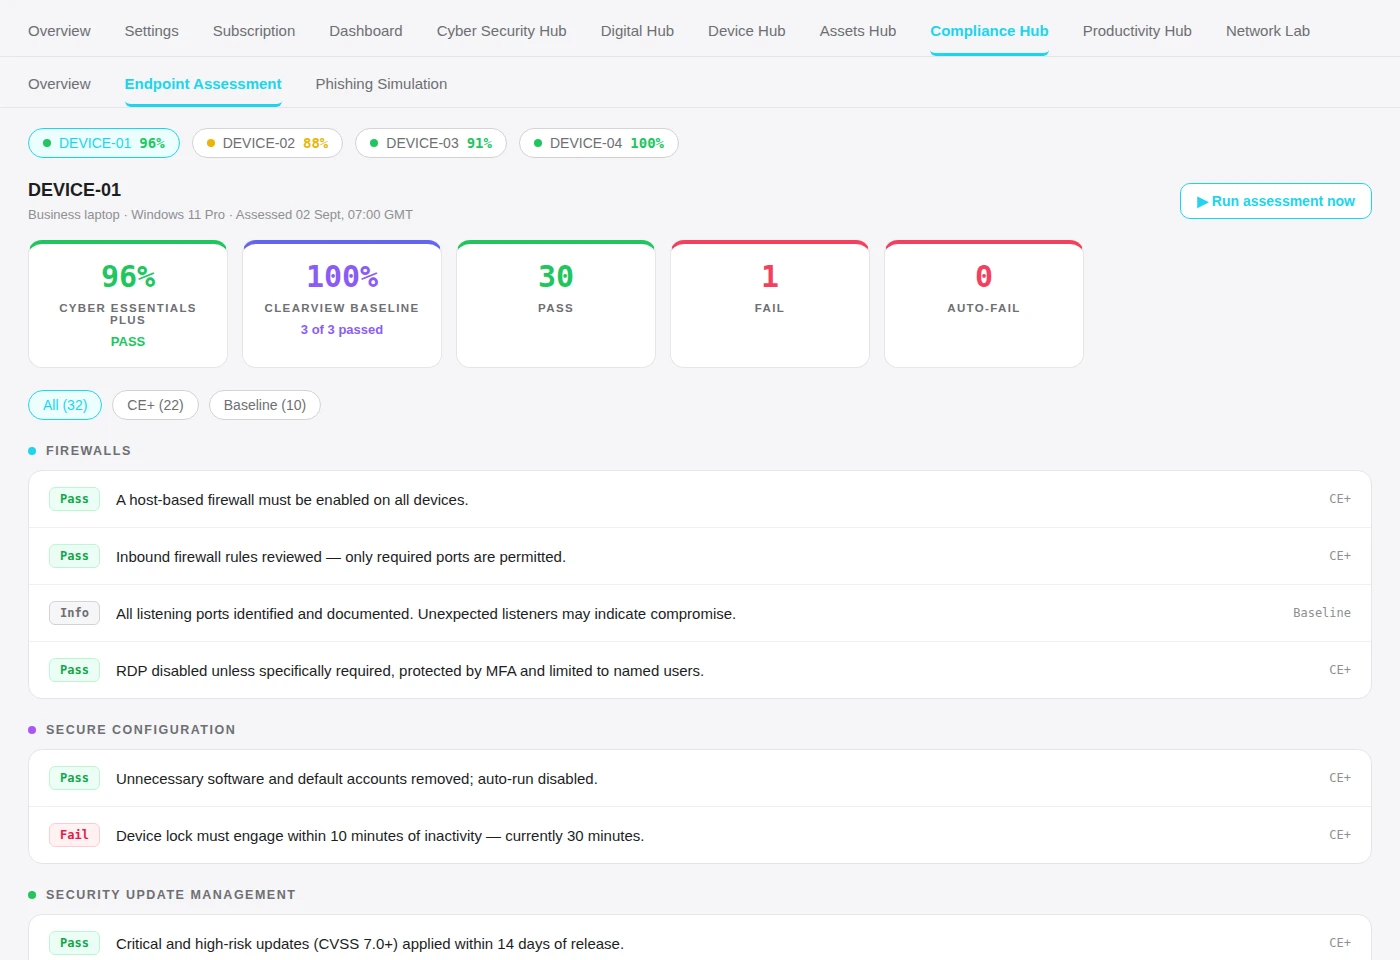
Endpoint assessment
every managed device tested against the Cyber Essentials Plus checks
Phishing simulation
click rate down, reporting up, and who needs a refresher
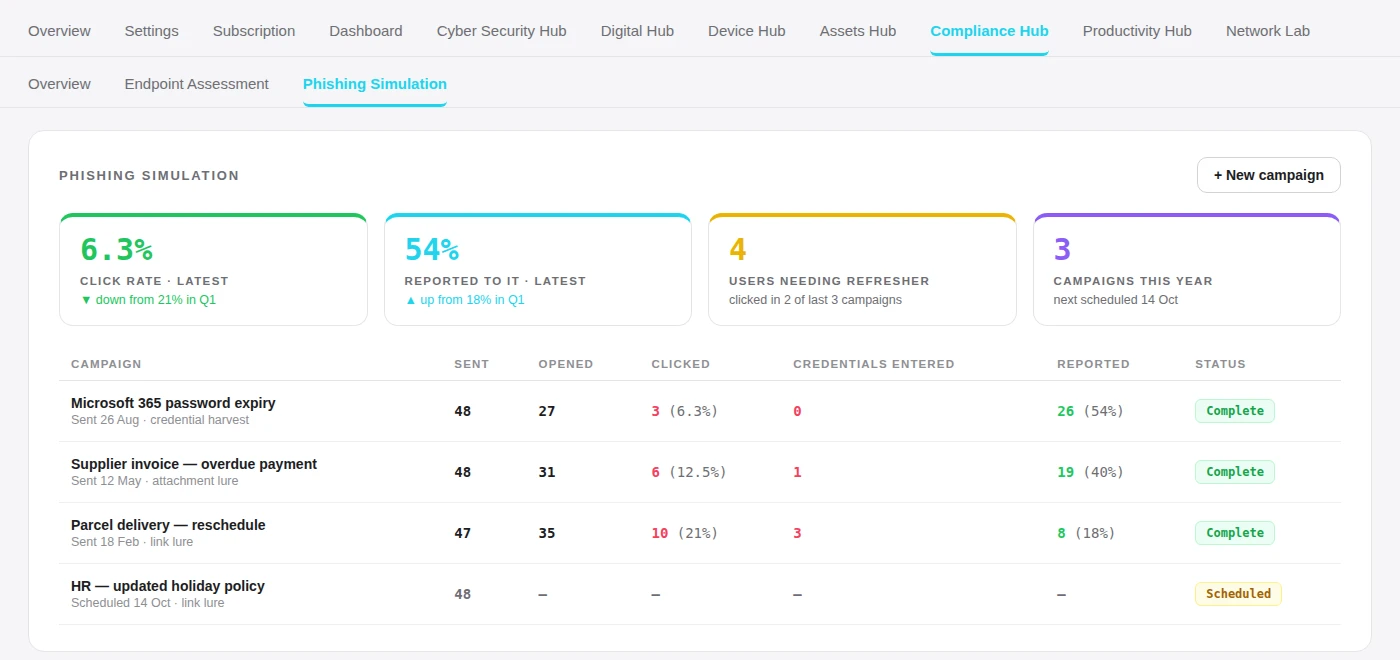
Layout is the real platform. Data shown is illustrative; client details are never published.
Four steps, none of them a scramble
See where you stand
The Compliance Hub shows Cyber Essentials, GDPR and ISO 27001 as a live posture: every requirement marked compliant, non-compliant, in progress or not yet assessed, with the gaps ranked by what will fail an assessment first.
Fix it, with the evidence collected as you go
Because we manage the devices and the Microsoft 365 tenant, most of the evidence is collected automatically: firewall state, encryption, patch age, MFA adoption, admin separation. Anything that needs a human decision is recorded as an admin attestation with an audit trail.
Pass the Plus test before the assessor arrives
Endpoint assessment runs the Cyber Essentials Plus checks on every managed device on a schedule: listening ports, device lock, patch age against the 14-day rule, malware protection, RDP and remote management. You see a pass or fail per device, in plain English, weeks before the real thing.
Keep it that way
Certification is annual; being secure is continuous. Posture is re-checked as devices and people change, phishing simulations keep staff sharp, and for ISO 27001 the built-in CISO Assistant holds your policies, risk register and Statement of Applicability so the management system stays alive between audits.
Where Clearview sits among compliance tools
Platforms such as Vanta, Drata and Secureframe are excellent for software companies with an engineering team and a SOC 2 audit ahead of them. Clearview is built for organisations whose IT we run, where the evidence already exists on the devices and the person fixing the finding is us.
| Questionnaire-only tools | Compliance automation platforms | Clearview by STG | |
|---|---|---|---|
| Where the evidence comes from | You answer questions and upload documents | API integrations into your cloud stack | The devices and Microsoft 365 tenant we manage, plus admin attestation |
| Who fixes what is found | You do | You do, guided by the platform | We do, as part of managed IT and security |
| Cyber Essentials Plus readiness | Not covered | Rarely covered; built for SOC 2 and ISO | Endpoint assessment runs the Plus checks on every device before the assessor |
| ISO 27001 | Templates | Strong, aimed at SaaS companies with engineering teams | CISO Assistant: policies, risk register, Statement of Applicability, 80+ frameworks |
| Staff awareness | Separate tool | Often an add-on | Phishing simulation built in |
The compliance practice
Cyber Essentials Certification
UK Government-backed certification against the five technical controls. We scope it properly, fix what needs fixing, and complete the Danzell self-assessment with evidence from the devices themselves.
Cyber Essentials Plus
The independent technical audit. We run the same checks the assessor runs (internal vulnerability scan, malware tests, MFA and admin separation, configuration review) on every device first, so the visit is a formality.
ISMS Design & Implementation
An information security management system that reflects how your organisation actually operates: scope, risk assessment, controls, Statement of Applicability, documented and ready for certification.
ISO 27001 Gap Assessment
Exactly where you stand against ISO 27001, requirement by requirement, with the gaps prioritised by risk and effort and a clear roadmap to Stage 1.
Policies & Procedures
Practical, enforceable policies your team will actually use. Held and versioned in CISO Assistant, mapped to the controls they satisfy, not stored as templates in a shared drive.
Risk Management & Asset Registers
A risk register that informs real decisions, with configurable scoring, treatment plans and an asset register fed by the Device Hub rather than maintained by hand.
Supplier & Security Assurance
Third-party assessments and supplier questionnaires handled once and answered from evidence, so customer due diligence stops being a week of your time.
Security Governance & vCISO
Senior security leadership on a fractional basis: board reporting, security strategy, internal audit and management review, without a full-time hire.
Audit Support & Evidence Packs
When the auditor arrives, the evidence pack already exists. We support interviews, walk-throughs and findings, for Cyber Essentials Plus and ISO 27001 Stage 1 and Stage 2.
Engagement options
One-off Assessment
A focused engagement to understand your current compliance posture. Ideal for organisations considering certification or needing a baseline review.
- Gap analysis against ISO 27001, Cyber Essentials, or other frameworks
- Prioritised findings report
- Remediation roadmap with effort estimates
Implementation Programme
End-to-end support building your ISMS from the ground up, through to certification readiness. We work alongside your team at a pace that fits your operations.
- Full ISMS build: scope, risk assessment, controls
- Policy and procedure development
- Internal audit and management review support
Ongoing Governance
Sustained compliance support after implementation. Keep your ISMS living and effective with regular reviews, updates, and fractional security leadership.
- Quarterly risk reviews and register updates
- Continual improvement programme
- vCISO and board-level reporting
Straight answers on certification
What is the difference between Cyber Essentials and Cyber Essentials Plus?
Cyber Essentials is a self-assessment against five technical controls, verified by a certification body. Cyber Essentials Plus adds an independent technical audit: an assessor scans a sample of your devices from inside the network, runs malware test files, checks MFA and admin separation, and reviews configuration against what you declared. Plus is what larger customers, insurers and public sector supply chains increasingly ask for.
What changed in the Cyber Essentials scheme in 2026?
The v3.3 Danzell question set went live on 27 April 2026. The headline changes: MFA is mandatory on every cloud service where it is available and its absence is an automatic fail; critical and high-risk vulnerabilities must be patched within 14 days; cloud services are formally defined and scoped; backups and passwordless authentication are called out. Remaining Willow accounts must be finalised by 26 October 2026.
How long does Cyber Essentials take?
For a business whose IT we already manage, the self-assessment is usually days rather than weeks, because the Compliance Hub already knows the state of every device and account. Cyber Essentials Plus adds the assessor visit, which we prepare for by running the same checks in endpoint assessment first. Starting from scratch with unmanaged devices, allow four to eight weeks for remediation.
Do you certify us for ISO 27001?
No, and neither does anyone honest. Certification is issued by a UKAS-accredited certification body after a Stage 1 and Stage 2 audit. We build the information security management system, run the risk assessment, write the policies, prepare the Statement of Applicability, run internal audits and management review, and support you through the audit. CISO Assistant inside Clearview keeps all of it maintained afterwards.
Do I need Clearview to get certified?
No. We can run a Cyber Essentials or ISO 27001 programme for an organisation whose IT we do not manage. Clearview makes it faster and keeps it true between assessments, because the evidence is collected from the devices themselves rather than from a questionnaire you fill in once a year.
What does a compliance engagement cost?
It depends on scope, device count and how far you are from the standard, so we quote per engagement. A gap assessment is a fixed fee; an implementation programme is priced against the remediation plan it produces. Cyber Essentials certification itself is a few hundred pounds paid to the certification body. Every engagement starts with a free, no-obligation conversation.
Compliance should reduce risk, not create paperwork
Whether you are renewing Cyber Essentials under the new question set, going for Plus, or building toward ISO 27001 — we should talk.
Discuss your compliance needs